

 Login

 October 6, 2026
|
Voiced by Amazon Polly |
Introduction
Quick Answer: A Claude API key is the credential that Anthropic issues through the Claude Console, allowing your application to authenticate and send requests to Claude models. You get one by creating a Console account at console.anthropic.com, adding a payment method, and generating a key under Settings, API keys. It starts with sk-ant- and appears only once, so you can copy it straight into a Secrets Manager secret or an environment variable. Getting one that works is easy. Getting one that is scoped correctly, rotated on schedule, and never sitting in your source code takes a bit more care, and that is what this guide walks through.
You wrote a quick script, pasted your Claude API key straight into the code, and it worked. Then someone pushed that code to a public repo, and by morning your usage dashboard looked like a crime scene.
It is a small string of text, but it carries real billing and data access. Treating it casually is how side projects turn into expensive lessons.
Master Claude AI for Next-Gen Applications
- Prompt Engineering
- Claude API
- Secure AI Development
What Is a Claude API Key and Why It Matters
It proves your application is allowed to talk to Claude models over the API. Every request you send, whether it is a chatbot reply, a document summary, or an agent-calling tool, needs this credential attached to the request header.
Without a valid one, the request bounces back with an authentication error, and nothing gets processed. With a valid credential, Anthropic can track usage, apply rate limits, and bill your account correctly.
Here’s the part beginners miss. This is not the same as your claude.ai login. If you already pay for Claude Pro or Max in the consumer app, that subscription provides a better chat experience, not programmatic access. The API and the Console are separate products built for developers, with their own account and their own key.
How to Get a Claude API Key From the Console
Getting one takes about five minutes once you know the sequence.
Step 1: Create a Console Account
Head to console.anthropic.com and sign up with your email or Google account. You will need to verify your phone number. This is separate from any claude.ai account you already have, even if you use Claude daily for chat.
Step 2: Add a Payment Method
The claude api is not free in the ongoing sense. Generating a key costs nothing, but every request is billed per token. New accounts sometimes get a small starting credit, but you still need a card on file before requests succeed at any real volume.
Step 3: Generate the Key
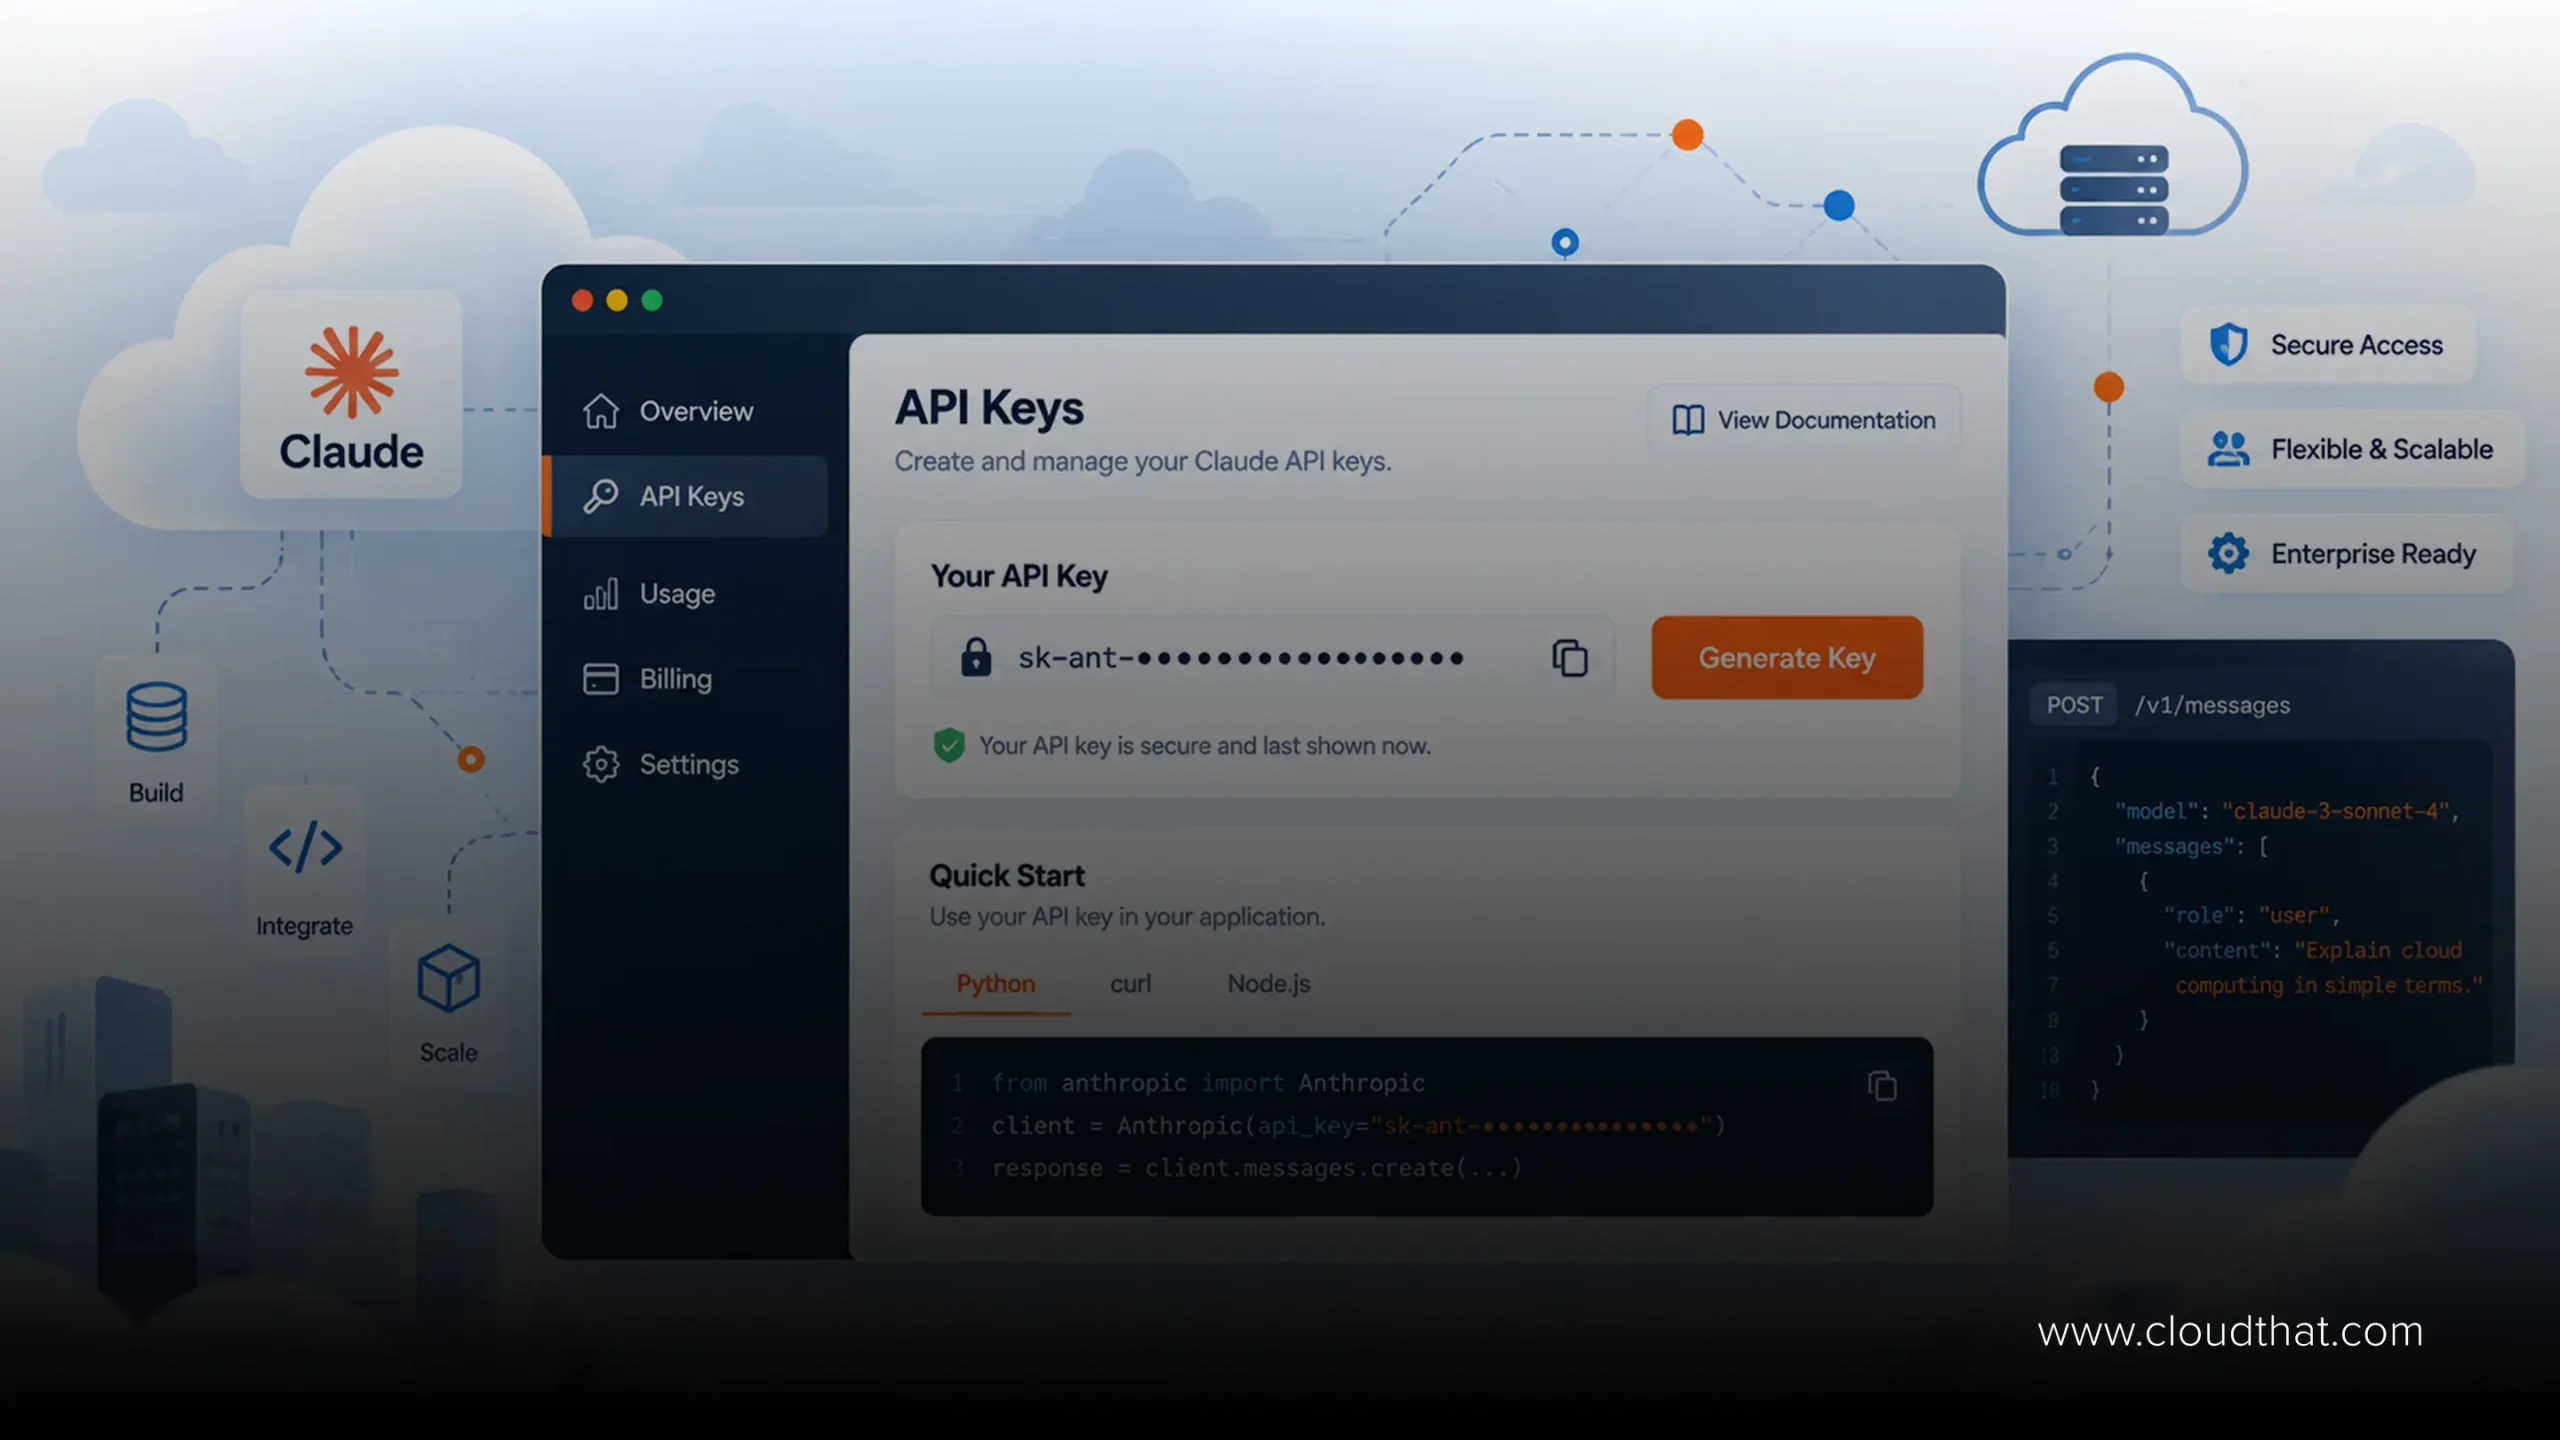
In the sidebar, go to Settings, then API keys. Click the button to create a new one, give it a descriptive name like “production-app” or “staging-env” so you can audit usage later, and pick the workspace it belongs to if you manage more than one.
Step 4: Copy It Immediately
Your Claude API key is shown exactly once, right after creation. It starts with sk-ant- followed by a long string of characters. Anthropic does not store the plaintext value anywhere you can retrieve later. Close that dialog without copying, and your only option is to revoke and generate a fresh one. Export it as an environment variable, and most SDKs read it automatically from there.
Key Types You Should Know About
Not every key should be used the same way, and this is where teams get sloppy.
Personal keys act as you individually. Fine for your own development work, but they stop functioning the moment you leave the organization, a bad fit for anything shared.
Service account keys represent a service account rather than a person. Use these for CI pipelines, production backends, or agents anything that should keep running after the engineer who set it up moves teams.
Workspace keys are a legacy option, tied to the workspace rather than an owner. They keep working indefinitely, which sounds convenient until nobody is accountable for a credential that outlives everyone who touched it.
For production, a service account key is almost always the right call.
How to Secure Your Claude API Key in Production
This is where the real damage happens, and it is rarely due to the key itself being weak. It is how teams handled it.
Never hardcode it. Do not paste your Claude API key directly into application code, notebooks, or config files that get committed to version control. Public scanners find exposed keys within minutes of a push, and by the time you notice, the damage is done.
Use secrets managers. Store it as a local environment variable. For production, move it into AWS Secrets Manager, HashiCorp Vault, GCP Secret Manager, or Azure Key Vault. These tools let you rotate credentials without redeploying code and give you an audit trail, a practice also outlined in OWASP’s API security guidance on credential handling.
Scope permissions tightly. When you create a key, you choose between full access and read-only access depending on the workload’s needs. A credential that only sends messages should not also hold admin rights over billing.
Set expiry where you can. Keys that never expire are keys nobody remembers to rotate. Build an automated process to cycle the key on a fixed schedule rather than leaving it valid forever.
Common Mistakes That Cost Teams Money
A few patterns recur with teams new to the Claude API.
Sharing one key across an entire team means you cannot tell whose script triggered a spike in usage when the bill arrives. Give each environment its own credential.
Reusing a development key in production is another classic. If it gets exposed during a demo or a screen share, your production traffic drops with it.
Skipping the anthropic-version header is smaller but common. It tells the API which response format to expect, and every request needs it alongside your key.
Calling the API With the SDK or Direct HTTP
Once your key is generated and stored safely, calling the API is straightforward.
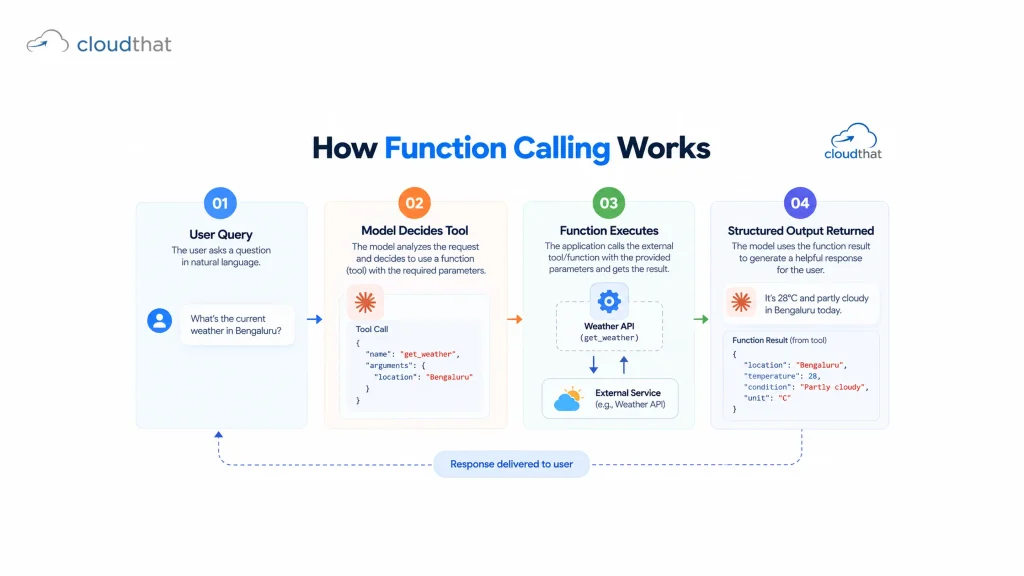
With the Python or TypeScript SDK, the client automatically reads it from the ANTHROPIC_API_KEY environment variable, so you rarely need to pass it manually. A basic request means initializing the client, picking a model, and sending a messages array.
Calling the API directly over HTTP means sending the key in the x-api-key header, the anthropic-version header, and your request body as JSON. This is common when wiring Claude into existing backend services or agentic workflows via Amazon Bedrock, where AWS IAM roles handle authentication instead of a standalone key.
Rotation and Expiry, Explained
Rotation is not optional once you are running anything that matters in production.
Automate a cycle, commonly every 90 days, to generate a new one and retire the old. Create the new key first, update your Secrets Manager, deploy, confirm it works, and only then revoke the old credential. Revoking too early breaks live requests mid-flight.
If a key is ever exposed, treat it as compromised and revoke it immediately rather than waiting for the scheduled rotation.
Why CloudThat Is the Right Place to Learn This Skill
Reading documentation gets you a working key. It does not get you a team that can build, secure, and scale AI applications with confidence, and that gap is where most GenAI projects stall.
CloudThat’s Claude Certified Developer, Foundations program takes engineers from generating their first credential to building production-grade applications with real authentication, secrets management, and observability built in from day one. It is hands-on labs, not a slide deck, where you generate keys, wire them into real applications, and practice the rotation and scoping habits this guide covers, under trainers who also run live AWS and GenAI engagements.
For teams building on Amazon Bedrock, CloudThat’s Generative AI with AWS consulting practice and the GenAI Innovation Center work directly with engineering teams on secure credential management and agentic workflows at scale. For an entire cohort rather than a single developer, the Capability Development Framework builds a custom learning path from zero to deployable within weeks, validated through Experiential Learning simulations.
CloudThat is an AWS Premier Tier Training Partner with 14+ years of cloud and AI training experience across 30+ countries, and its trainers run live GenAI and Bedrock engagements, not just slides. The AWS Mastery Pass and the AWS Partner Acceleration Training Program are built for exactly that jump, and you can check upcoming batches on the training calendar.
Conclusion
A Claude API key looks simple: one string of text. But how you get it, store it, scope it, and rotate it decides whether your AI application is production-ready or one leaked screenshot away from a very bad week. Get the basics right early, and the rest of your integration becomes much easier to trust.
Key Takeaways:
- A Claude API key authenticates your application to the Claude API and is separate from any claude.ai chat subscription.
- Generate it through the Console at console.anthropic.com after adding a payment method.
- It is shown only once at creation, so copy it into Secrets Manager immediately.
- Personal keys suit individual development, while service account keys are best for production workloads.
- Never hardcode the key into source code or commit it to version control.
- Use a proper Secrets Manager rather than plaintext config files for any production credential.
- Scope each key’s permissions to only what the specific workload requires.
- Rotate it on a fixed schedule, commonly every 90 days, and immediately after any suspected exposure.
- Give each environment or service its own credential instead of sharing a single credential across a team.
- Amazon Bedrock users authenticate using AWS IAM rather than a standalone key.
Ready to build production-grade skills instead of just reading about them? Explore CloudThat’s Claude Certified Developer, Foundations training and start building with real labs, not just slides.
Advance Your AI Career with Claude AI
- Enterprise AI Skills
- Claude API
- AI Assistants
About CloudThat
FAQs
1. Is a Claude API key the same as my Claude Pro subscription?
ANS: – No. Claude Pro or Max on claude.ai is a better chat experience for personal use. This credential is issued by the separate Console and is required for programmatic access.
2. How much does it cost to generate a key?
ANS: – Generating it is free. Using the claude api is billed per token, and you need a payment method on file before requests succeed at scale.
3. Can I use the same key across multiple applications?
ANS: – You can, but it is not recommended. Separate keys per application make usage tracking, rotation, and incident response far easier.
4. What happens if my key gets exposed publicly?
ANS: – Revoke it immediately in the Console. Anthropic cannot show you the secret value again, so generate a fresh one and update it everywhere the old key was used.
5. Do I need a key to use Claude through Amazon Bedrock?
ANS: – No. Bedrock authenticates using AWS IAM roles and credentials rather than a standalone key.
6. How often should I rotate my Claude API key?
ANS: – Most teams rotate every 90 days, or immediately if a key is suspected compromised. A Secrets Manager can automate this.
7. Where can I find official documentation for the claude api?
ANS: – Anthropic maintains it at the Claude Platform Docs, alongside the AWS Bedrock documentation for teams accessing Claude through AWS.
WRITTEN BY Himisha Raval
Himisha Raval is a Digital Marketing Manager at CloudThat with a strong command of search engine optimization, web analytics, link building, and content strategy. She brings a data-driven approach to digital marketing, helping IT companies strengthen their online presence, improve search rankings, and generate consistent leads across channels. Beyond execution, she plays an active role in ideation, campaign strategy, and website performance optimization. Outside of work, she balances her analytical side with a love for travel, nature painting, and dancing.


 PREV


Comments